Systems | Development | Analytics | API | Testing

The eMudhra certificate compromise: how it affects Bitrise users

On October 17, 2026, the developer world learned that the private keys of eight intermediate certificate authority (CA) certificates from eMudhra had been compromised. In this article, I’ll explain how that affects the Bitrise environment powering your Bitrise CI jobs, Build Hub runners, and Remote Developer Environments.
6 Vibe Coding Security Tools for Enterprise Engineering Teams

AI coding assistants are changing how enterprise software gets built. Developers can generate applications, refactor code, install dependencies, and connect external services through natural-language instructions. But the same tools that accelerate development can also access sensitive files, execute commands, and introduce unverified components into corporate environments.

The Security Domino Effect: Why Trust Can't Be an Afterthought in AI

In interconnected software environments, a security vulnerability rarely exists in isolation. A weakness in one component can expose credentials, create unintended access paths, or give attackers a foothold in connected services. The consequences depend on what that component can access, the permissions it holds, and the safeguards around it. As organizations adopt cloud platforms, third-party integrations, and AI-powered development tools, the boundaries between systems matter more than ever.

Why API Security Is Foundational to AI Security (Akamai Study)

Secure AI starts with securing the APIs underneath it. This session breaks down why APIs and MCPs are the control plane for AI apps and agents, where unmanaged API risk hides, and how security and platform teams can improve visibility, posture, runtime protection, and governance across production environments. KEY TAKEAWAYS TIMESTAMPS.

Healthcare IAM Trends: What's Shaping Identity Security in 2026

‍Healthcare identity and access management (IAM) controls access to clinical systems and patient information. It governs authentication, authorization, account provisioning, and access removal across connected healthcare environments. Healthcare IAM trends reflect expanding access requirements across employees, vendors, applications, and AI agents. Each identity needs defined permissions, accountable ownership, and monitoring appropriate to its operational role.

Multi-Factor Authentication in Healthcare: Balancing Security and Clinical Speed

‍ Multi-factor authentication verifies user identity through two or more distinct authentication factor categories. These include something users know, possess, or inherently are, such as biometric characteristics. The multi-factor authentication healthcare organizations deploy protects electronic health records, remote access, and clinical applications. Healthcare authentication must accommodate shared workstations, frequent user changes, and time-sensitive clinical tasks.

Agentic AI Security and Governance: Risks, Controls, and a Practical Checklist

Agentic AI security is the set of controls that keep AI agents from accessing, changing, or sharing more than they should. It covers who an agent acts for, which data and tools it can use, which actions need approval, and how its activity is recorded and reviewed. AI agents are moving from pilots into daily operations. They read invoices, update records, answer customers, and trigger workflows across business systems.

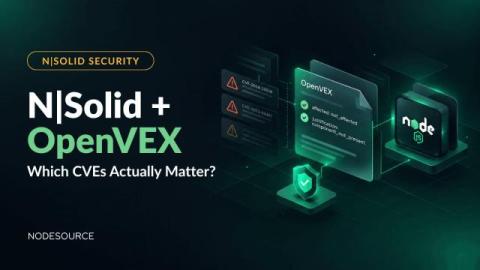
Not Every CVE Is Exploitable: How N|Solid Uses OpenVEX to Add Security Context

Finding a vulnerability is only the beginning. Modern applications depend on hundreds or even thousands of software components, and vulnerability scanners are essential for identifying known security issues across those dependencies. But there is a problem: the presence of a vulnerable dependency does not always mean your application is actually exploitable.

Device-centric threat intelligence and where to find it

TLDR: Device specific threat intelligence is provided by using device specific threat intelligence platforms like PCA Cervus that look at component level risks. Device-centric threat intelligence is threat intelligence that focuses specifically on risks to a connected device like a point of sale terminal or a card reader. This post explains what device centric threat intelligence is and how it differs from traditional SOC centric threat intelligence and what to look for in threat intelligence feed so you can be sure it gives device centric intelligence vs generic SOC focused intel.

Threat intelligence For Products Explained

TLDR: Product threat intelligence comes from using product specific threat intelligence platforms like PCA CERVUS and is specific to individual products and their parts. Most threat intelligence platforms are built for security operations centres (SOCs) and thus they track attacker infrastructure and campaigns aimed at corporate networks. These platforms are designed to help an SOC defend an organization and give the TTPs needed to run red teaming or pen testing against these environments also.