Systems | Development | Analytics | API | Testing

Performance Testing Security: A 2026 Imperative

Performance testing security in isolation is no longer sufficient. Security vulnerabilities often emerge under peak load, when systems are most exposed. Testing for both performance and security, together and under stress, is now a baseline requirement for organizations that prioritize resilience.
From Dashboards to AI Agents: Huel's Analytics Journey

You’ve rolled out a modern data stack, built self-service dashboards, and empowered your team to ask their own questions. Job done, right? Not quite. The data landscape is shifting rapidly beneath our feet, which makes it critical to understand how to build your AI for BI platform so you can scale and navigate technology evolutions.

Insurance Workflow Automation: From RPA to Straight-Through Processing - The 2026 Maturity Model

Insurance workflow automation connects data, applications, business rules, and approvals across insurance operations. It reduces manual handoffs across claims, underwriting, billing, and policy servicing the same discipline behind Zymr’s work in the adjacent fintech and BFSI space. RPA automates repetitive tasks but cannot manage complex, end-to-end decisions independently.

What Should Digital Creators Look for in Gumroad Alternatives?

Look for fair fees, room to sell more than one type of product, and tools that help you actually promote what you sell. Gumroad works fine when you're starting out, but the cut it takes grows right along with your sales. That's usually the moment creators start looking elsewhere.

Best SOC automation tools for different use cases

The SOC automation tool market has become crowded quickly with a variety of platforms and tools on offer. Some platforms automate alert triage while others claim to investigate incidents across multiple tools. Also different is how the tools actually work in the backend and the experience of the SOC relying on them i.e some tools are still built around deterministic predefined workflows. However there is also a newer group of SOC automation tools like Legion Security that build on agentic security platforms.

Boosting API Throughput for Financial Platforms

The most effective way to improve API throughput is a pragmatic mix of measurement, understanding provider constraints, and targeted engineering fixes. Always weigh throughput gains against their impact on reliability and user experience. Sustainable performance comes from addressing bottlenecks at every layer, not just tuning the API in isolation.

RAG in Quality Engineering: Ship Faster, Test Smarter | Janani Balasubramanian

How can Retrieval-Augmented Generation (RAG) help Quality Engineering teams ship faster and test smarter? In this TTTribeCast session, Janani Balasubramanian explores the practical applications of RAG in Quality Engineering and how teams can use organizational knowledge, testing data, and engineering context to improve the way they design, prioritize, and execute testing.

Guide to Load Testing Multi-Tenant SaaS Applications (2026)

Multi-tenant SaaS applications require a fundamentally different approach to load testing. Standard scripts that ignore tenant boundaries often miss critical issues. Tenant-aware load testing is essential for accurately measuring both overall performance and the integrity of data isolation. Without this, subtle forms of cross-tenant data leakage or resource contention may go undetected, especially under realistic, mixed-tenant workloads.

Team-Based DLP: Give Each Group Its Own Redaction Rules

A shared Kubernetes cluster rarely belongs to one team. Payments runs checkout in one namespace, search runs search-api in another, and a risk team runs a scorer somewhere else. One Speedscale forwarder captures API traffic for all of them. Redacting that traffic before it leaves the cluster is what makes it safe to use for testing (the background is in The PII Testing Dilemma). Until now, that forwarder ran exactly one DLP rule. Every team that needed a field redacted had to edit the same JSON document.

Governed Data Pipelines: Meeting SOC 2 and Regulatory Requirements

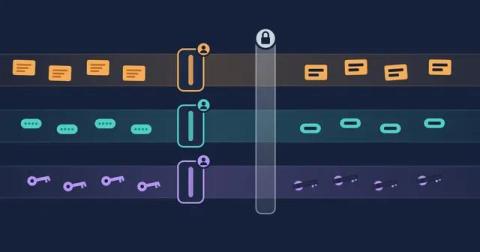
Organizations moving healthcare, financial, or EU-resident data through an ETL pipeline face a specific constraint: the pipeline itself has to be compliant, not just the destination warehouse. Every hop a record makes from source system to transformation layer to warehouse, is a point where sensitive data can be exposed, mishandled, or logged somewhere it shouldn't be. That makes the governance model of the pipeline tool itself part of the compliance picture, not an afterthought to it.